

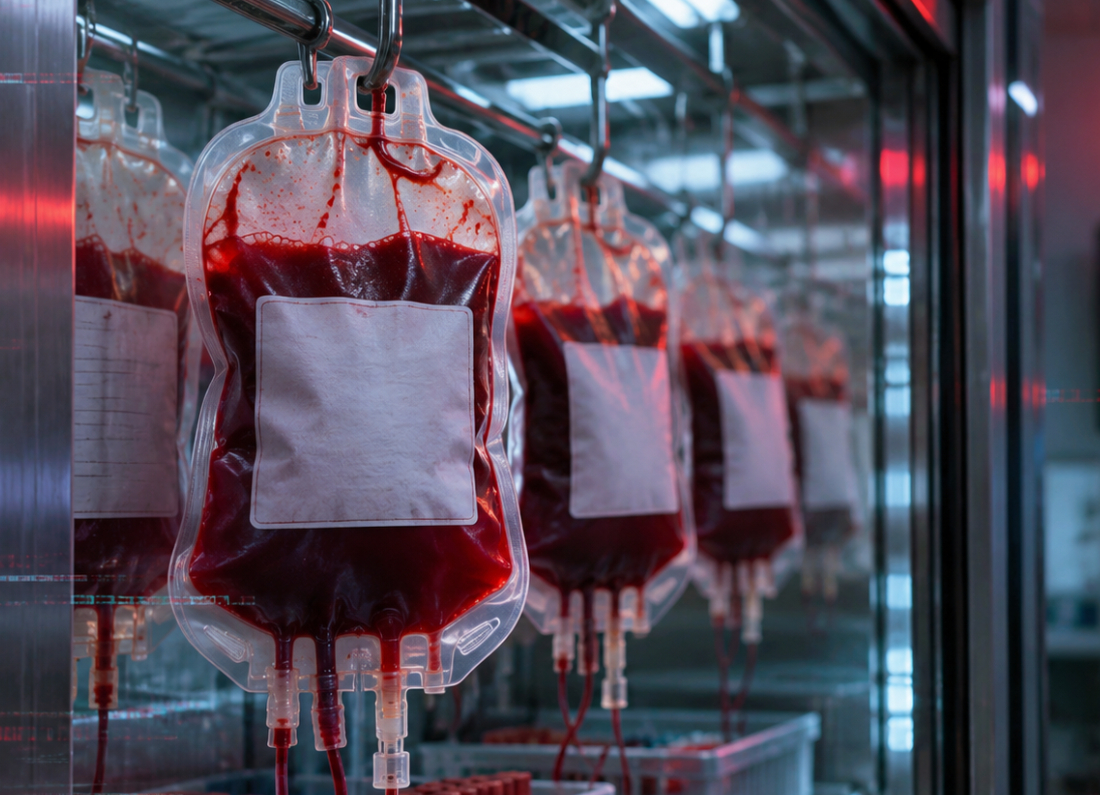
Hackers have attempted to interfere with vital blood supplies in France after gaining access to refrigeration systems at three facilities, raising temperature controls to dangerously high levels in an incident that should serve as a warning about the extraordinary vulnerability of Europe’s essential infrastructure.
France’s national blood service, the Établissement français du sang (EFS), confirmed that the attack took place on Monday 2 November and affected cold-storage equipment operated by an external supplier.
The attackers altered temperature and defrost settings at three facilities containing plasma intended for medical treatment and the production of medicines.
Fortunately, monitoring systems detected the changes before any blood products were compromised. Staff intervened, secured supplies and transferred products to unaffected storage facilities.
No blood products were lost, no health consequences have been identified and blood collection and distribution continued uninterrupted.
That is the good news. The deeply uncomfortable question is what would have happened if those alarms had failed, or if the attack had struck somewhere without sufficient staff, monitoring or alternative storage capacity.
Because this was not simply an attempt to steal information from a database. It involved manipulating the physical conditions in which medical supplies essential to saving lives are stored.
And the circumstances reveal a problem that governments across Europe can no longer afford to treat as somebody else’s responsibility.
When an attack on a supplier threatens a public health service
The French blood service performs a function that should never be confused with an ordinary commercial operation.
It collects, tests, prepares and distributes blood products to more than 1,900 hospitals, supporting the treatment of over a million patients every year.
Blood and plasma supplies are essential to emergency medicine, major surgery, cancer treatment and the care of people with serious illnesses.
They require careful handling, reliable transport and strictly controlled storage conditions.
If those conditions are compromised, products may become unusable. That can mean wasted donations, additional pressure on already stretched services and potential consequences for patients depending on a reliable supply.
Yet the vulnerability exploited in France was not, according to EFS, within the blood service’s own directly operated systems.
The incident affected refrigeration equipment provided by a contractor.
The distinction is important. A public health institution can invest heavily in protecting its own computer networks and still find its operations exposed through a commercial supplier.
When essential infrastructure depends on a chain of external companies, the security of the whole system is only as strong as its weakest link.
The refrigeration provider Coolworld has acknowledged a cybersecurity incident affecting a limited number of its units, saying the vulnerability concerned a third-party component outside its direct control.
That explanation illustrates the problem rather than resolving it.
A supplier points to a component manufacturer. A component manufacturer may point to a software provider. The organisation delivering a vital public service is left managing the consequences.
Whatever the contractual arrangements, it is the public that ultimately depends on the equipment working.
Europe has already seen the consequences in its supermarkets
The French blood-storage incident occurred during a much wider wave of attacks on refrigeration systems across Europe.
Supermarkets in several countries have reported hackers remotely manipulating cooling equipment, forcing temperatures upwards and causing food to spoil.
The incidents have affected retailers in countries including Belgium, Ireland, the Netherlands, Sweden and Luxembourg, with further disruption reported elsewhere.
In France, hundreds of supermarket refrigeration systems were reportedly compromised during attacks in October.
The economic consequences have been substantial.
Food worth millions of euros has been damaged or destroyed, while businesses have faced the additional costs of restoring equipment, replacing stock and investigating how the attacks occurred.
These are not abstract losses occurring somewhere in the digital economy.
They are physical goods that people produced, transported, stored and expected to buy or consume.
When refrigeration systems are compromised, food can become unsafe and entire supply chains can be disrupted.
The escalation from supermarket refrigeration to facilities holding blood products demonstrates how similar technological weaknesses can affect sectors with very different consequences.
A supermarket losing its frozen stock is a serious economic problem. A hospital losing access to essential medical supplies could become a public health emergency.
The French blood service prevented that outcome. But its success should not be mistaken for proof that the underlying problem is under control.
The uncomfortable reality behind the promise of technological efficiency
For years, governments and businesses have been encouraged to connect more of their operations to the internet.
Equipment can be monitored remotely, faults can be identified without engineers attending every site, and systems can be adjusted from a central location.
There are genuine advantages to this technology.
But the promise of greater efficiency has too often been discussed without equivalent attention to the risks created when essential physical infrastructure becomes remotely accessible.
The same system that allows an authorised technician to change refrigeration settings can become dangerous if someone else obtains access.
Security therefore cannot be treated as an optional additional cost, something to address when a company has sufficient spare money or after a breach has already occurred.
It is part of the infrastructure itself.
A hospital would not regard fire protection as an optional feature of a blood-storage facility. Nor should reliable cybersecurity be regarded as a secondary concern.
Yet the evidence from Europe’s recent attacks suggests that important systems are still operating with vulnerabilities that should have been addressed.
Outdated software, insecure remote access and weak credentials have all been identified as risks in connected industrial equipment.
The British government’s own cybersecurity authorities have warned that attackers are exploiting familiar, preventable weaknesses rather than relying entirely on exotic new techniques.
This is a failure of priorities as much as a technical problem.
If the financial advantages of digital infrastructure are pursued without ensuring that its security is properly funded, the savings are being achieved by transferring risk elsewhere.
And when the infrastructure supports healthcare, food supply or public utilities, that risk is transferred to society.
Britain’s cybersecurity chief has issued a stark warning
The danger is not confined to France.
Speaking at the launch of the National Cyber Security Centre’s annual review on 3 November, its chief executive Richard Horne warned about the exposure of systems that are not traditionally regarded as information technology.
He highlighted electricity switching, water facilities, manufacturing equipment, heating and refrigeration controls.
These are the systems that make modern life function.
Horne warned that their security and resilience are frequently overlooked in investment decisions, despite their growing exposure to cyberattacks.
It was a particularly timely intervention.
British food suppliers have also been affected by the recent refrigeration incidents, although the UK’s National Cyber Security Centre said the overall domestic impact remained limited.
The agency has separately warned that artificial intelligence is likely to increase the speed and scale of cyberattacks against critical infrastructure.
Its 2026 annual review assesses that AI-powered malware is highly likely to be used in a ransomware attack on Britain’s critical national infrastructure by 2028.
But it would be misleading to suggest that the French blood-service incident has been established as an AI-enabled attack.
There is no evidence in the reporting that artificial intelligence was involved.
The wider warning is that attackers do not need revolutionary technology to exploit systems that are already insufficiently protected.
AI may accelerate the process, but neglected security has been a problem for years.
Nobody knows who was responsible
The timing and geographical spread of the attacks have prompted speculation about whether they could form part of a wider campaign of sabotage.
European governments are already concerned about hostile cyber activity, particularly in the context of Russia’s war against Ukraine and growing tensions between Moscow and Western countries.
Some cybersecurity specialists have suggested that the incidents could represent an attempt by a state-linked actor to demonstrate its ability to disrupt European infrastructure.
Others have raised the possibility of independent hackers exploiting available vulnerabilities.
At present, neither explanation has been established.
No group has publicly claimed responsibility for the French blood-storage attack, and the authorities have not identified its perpetrators or confirmed their motive.
That uncertainty matters.
The temptation to attribute every alarming cyber incident to a familiar geopolitical adversary may be politically convenient, but serious journalism requires evidence.
If a hostile government is responsible, the public deserves to know.
If criminal groups or individual attackers are exploiting widely available weaknesses, the public deserves to know that too.
The urgent issue is not finding a politically useful enemy before the investigation is complete.
It is establishing how access was obtained, why the systems were vulnerable and how to prevent the same thing happening again.
Public safety cannot depend on the cheapest available contract
There is a wider political argument that deserves more attention than it usually receives.
Governments have spent decades relying on private contractors to provide, operate and maintain parts of essential public infrastructure.
Contracting itself is not proof of negligence, and the French incident does not establish that the procurement arrangements were improper or that any company breached its legal duties.
But outsourcing creates relationships in which responsibility can become fragmented.
The public authority depends on a supplier. The supplier depends on software and equipment providers. Individual organisations may have very different security standards, budgets and technical capabilities.
When something fails, the consequences are experienced by people who had no part in negotiating those contracts.
This is why cybersecurity for essential services needs enforceable standards, independent scrutiny and clear accountability across the entire supply chain.
It is not enough for a provider to promise that it takes security seriously.
Governments should be able to demonstrate that equipment supplying essential services is regularly tested, maintained and capable of operating safely when remote connections are compromised.
Contracts should establish who is responsible for applying security updates, monitoring vulnerabilities and maintaining workable emergency procedures.
Public bodies also need sufficient funding and technical expertise to assess their suppliers, rather than relying entirely on assurances from the companies selling them equipment.
And there must be a credible expectation that essential systems can continue operating when connected technology fails.
That might involve independently monitored alarms, physically separated backup systems or the ability to disconnect vulnerable equipment without losing control of vital operations.
The French blood service appears to have benefited from precisely the kind of monitoring and emergency response that can prevent an incident from becoming a disaster.
Other organisations may not be so fortunate.
The people who prevented the damage deserve recognition
There is one aspect of this story that should not be lost in the debate about cybercriminals and corporate accountability.
The staff responsible for protecting France’s blood supplies acted quickly enough to prevent harm.
Monitoring systems raised the alarm. Technicians intervened. Stored products were secured or moved elsewhere.
The result was that hospitals continued receiving the supplies they needed, and patients were not placed at risk by damaged blood products.
That response matters because it demonstrates why investment in resilience works.
Security is not simply about stopping every attacker from gaining access. It is also about ensuring that when something goes wrong, a service can detect the problem, limit the damage and continue functioning.
Those protections require planning, training, equipment and people.
They also cost money.
The tendency to treat staffing, maintenance and backup systems as expenses to be minimised becomes considerably harder to defend when their absence could put human lives at risk.
France avoided losing its blood supplies because safeguards were in place and people were able to act.
That should strengthen the argument for investment, not encourage complacency.
Europe needs to decide what essential infrastructure is worth
The attack on France’s blood service should force a change in how politicians discuss cybersecurity.
It is no longer sufficient to imagine cybercrime as somebody stealing passwords, leaking emails or demanding a ransom from a business.
Connected technology now governs parts of the physical world.
It controls temperatures, power systems, manufacturing processes and equipment used by essential public services.
That makes cybersecurity a question of public health, economic security and political responsibility.
It also raises difficult questions about the balance between efficiency and resilience.
A system may be cheaper to operate when everything is connected and remotely controlled. But if that arrangement exposes essential services to preventable interference, the apparent saving may be illusory.
The costs only become visible when an attack succeeds.
In France, the immediate consequences were contained. No blood products were lost and no patients were harmed.
Across Europe’s supermarkets, the consequences have already included substantial destruction of food and economic losses.
The same underlying vulnerability can therefore produce very different outcomes depending on what the equipment is protecting and how effectively an organisation responds.
There is no evidence yet identifying who carried out the attacks, and no basis for claiming that Europe’s blood supplies are currently in widespread danger.
What the incident does demonstrate is that a system essential to healthcare was exposed through equipment outside the direct control of the public service using it.
That should be enough to prompt serious examination of how critical infrastructure is procured, secured and maintained.
The warnings from Britain’s National Cyber Security Centre are equally clear: too many essential systems remain vulnerable, and cyberattacks are becoming faster and more consequential.
France was fortunate that its alarms worked.
Europe cannot build its approach to public safety around the assumption that they always will.


Leave a Reply